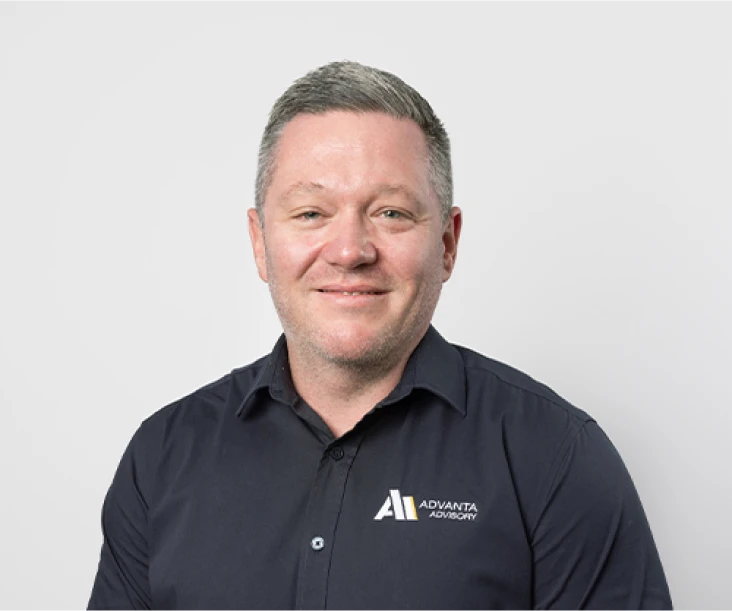
Adam Cliffe
Education:
20+ years in IT, cyber security and governance, MAICD, MACS Snr CP (Cyber Security)
Adam Cliffe
Director, Governance, Risk and Compliance at Advanta Advisory
Privacy & Cyber Security Advisor | GRC Specialist
Education:
20+ years in IT, cyber security and governance, MAICD, MACS Snr CP (Cyber Security)
Certifications & Accreditations
- MACS Snr CP (Cyber Security), Australian Computer Society, June 2024
- Cybersecurity Technologies, La Trobe University, November 2022
- Open Source Intelligence (OSINT) Fundamentals, TCM Security
- PRINCE2 Foundation, APMG
- ITIL v3 Foundation, ISEB
- Apple Certified Associate
- ISC2 - Certified in Cyber security
Organisation Memberships
- Australian Institute of Company Directors, Member (MAICD)
- Australian Information Security Association (AISA), Member
- ISC2 Member
- Australian Computer Society
- IAPP Member
Bio:
Adam Cliffe is the Founder and Director, Governance, Risk & Compliance at Advanta Advisory. He leads the firm’s work across governance, risk and compliance, privacy, cyber security, data governance and AI governance, giving boards and executive teams across Queensland clarity around their risks and confidence in the decisions they make.
Adam has a simple test for any organisation he works with: Show him the policy, then show him the policy in effect. In his experience, the gap between the two is where real risk sits, whether that’s a data retention policy that has never deleted a record or a breach response plan that has never been tested.
That practical perspective comes from more than 20 years of hands-on leadership and operational experience in technology.
He began his career as a field engineer and went on to deliver ICT infrastructure for major capital projects across Australia, Asia and the UK. As SEQ Managing Director at ADITS, Advanta’s sister company, he worked closely with not-for-profit, medical and professional services organisations, aligning technology and cyber security in a balanced, practical, privacy-first approach. He knows how effective controls work in practice and is quick to remind leaders that attackers rarely hack in, they log in.
He has little time for compliance theatre or reports you can’t read. His advice brings clarity to complex issues, giving boards and leaders the insight they need to make informed decisions with confidence.
Adam shares his perspective through executive briefings, industry events and media commentary, including presentations to the Australian Computer Society and an interview with Sky News Australia. He has also contributed to the Australian Signals Directorate’s consultation on the future of the Essential Eight in 2026.
Articles by Adam Cliffe
Vendor Risk Management. How to Build an Effective Programme
You’ve been handed the job of building a vendor risk management programme. Your board, auditor or insurer wants to see…
View More
AI Advisory in Australia, the Case for Slowing Down First
QUICK SUMMARY Core verdict: Choosing an AI tool is the fast decision, working out who’s accountable for it is the…
View More
Cyber security assessment and the signals your business needs one
QUICK SUMMARY Core verdict: A cyber security assessment turns assumption into evidence. The businesses reading the signals early are the…
View More
How to Build a Vendor Risk Assessment Framework That Works
Most businesses rely on dozens of third-party vendors. Payroll platforms, managed IT providers and cloud storage services just to start.…
View More
Cyber Security Consulting in Brisbane, the Advanta Approach to Managing Risk
QUICK SUMMARY Core verdict: IT support and cyber security consulting are two different jobs. Good IT support keeps your systems…
View More
GRC Consulting Explained, for the Moment Someone Asks You to Prove It
QUICK SUMMARY Core verdict: GRC consulting is worth it the moment a client, an insurer or a regulator asks you…
View More
Why Is Data Governance the Foundation of GRC?
What’s Covered: What role data governance plays in GRC How to tell if your data governance is holding back your…
View More
How to Build an AI Governance Framework in Australia
Most AI governance conversations start with frameworks and flowcharts. This one won’t. Most leaders we talk to aren’t confused about…
View More
Your business continuity plan is due a reality check
Your business continuity plan was thorough when it was written. When was that, exactly? Three years ago? Four? The person…
View More
Your AML/CTF privacy obligations go further than most reporting entities expect
From 1 July 2026, a new category of Australian businesses became subject to Anti-Money Laundering and Counter-Terrorism Financing Act 2006…
View MoreWork With Our Team
If you’d like to talk through your organisation’s privacy, cyber security or governance obligations with an advisor who understands both the technical and leadership sides, we’re happy to have that conversation. Learn more about how Advanta Advisory supports organisations like yours.
Contact us today